
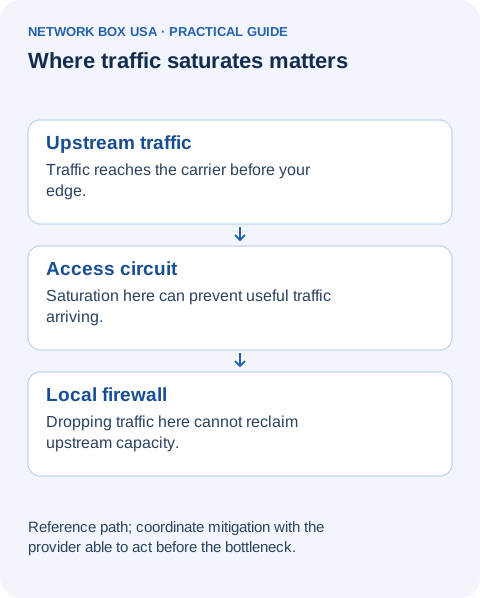
A firewall can block unwanted traffic and still leave a business unreachable during a distributed denial-of-service (DDoS) attack. If attack traffic fills the internet connection before reaching the firewall, dropping those packets at the office cannot recover the capacity they already consumed. Protection for that bottleneck needs to operate upstream, before traffic enters the constrained link.
For IT directors and MSPs, the useful buying question is where each protection takes effect. A gateway's DDoS feature, an internet provider's mitigation service, and application controls address different resources. Start by identifying what could run out of capacity and who can act there.
URL-based request filtering can help defend web applications against certain DDoS attacks. Network Box USA's managed WAF+ provides application-aware rules, while UTM+ protects the network gateway. Neither capability alone establishes protection against saturation upstream of its deployment point.
Follow the traffic to the first bottleneck
Consider a hypothetical office that hosts a customer portal behind a managed firewall. The portal and employees share one internet circuit. During a large incoming traffic flood, the firewall may continue rejecting unwanted packets while customers cannot load the portal and staff struggle to use cloud applications.
The critical distinction is location: filtering happens after the shared circuit has carried the traffic. Replacing the firewall with a faster model may improve processing capacity at the office, but it does not enlarge or clear the upstream connection. The same reasoning applies when evaluating a hosting provider's network boundary.
The UK's National Cyber Security Centre explains that network links, computing resources, and storage can each become exhausted. It also notes that services sharing a link can affect one another and that an overloaded management path can prevent administrators from reaching systems. These are separate dependencies to map before an incident.
Match the response to the resource under pressure
A service outage alone does not establish a DDoS attack. Legitimate demand, an application fault, or a routing problem can produce similar symptoms. The NCSC's response guidance recommends interpreting traffic and system measurements before choosing a defense.
| Observed pressure | Evidence to compare | Response to evaluate |
|---|---|---|
| The internet circuit is saturated | Provider-side utilization, traffic patterns, and delivery loss | Filtering or traffic cleaning before the constrained connection |
| The gateway struggles while bandwidth remains available | Packet and connection rates, device resource use, and security events | Gateway protections, policy, capacity, and upstream assistance |
| The application is overloaded | Request patterns, response times, server load, and database activity | Application-aware filtering, rate limits, and application capacity |
This table is a starting point for investigation, not a diagnosis. More than one resource can be under pressure. Pair the gateway view with provider and application evidence so that a local dashboard does not become the only account of the outage.
Make upstream protection a defined service
The NCSC's upstream defense guidance describes ISP filtering and packet-scrubbing services, which attempt to separate unwanted traffic from traffic that should continue to the customer. Providers differ in their capabilities and commercial terms.
Before relying on that coverage, establish which public addresses and services are protected, where traffic is filtered, and which attack types the arrangement addresses. Confirm whether mitigation is always active or requires an authorized request, how activation works, and what the provider commits to during that transition.
Also establish what happens when the provider protects its wider network by restricting your service. Discarding all traffic to an affected destination may contain the wider impact while leaving that destination unavailable. The recovery procedure, notification path, and any additional charges belong in the discussion alongside the protection itself.
Keep application protection in its proper place
Network Box USA's UTM+ provides Layer 3 DDoS protection at the network gateway, alongside managed firewall and intrusion prevention controls. It can filter unwanted network traffic and enforce security policies. If deployed behind a saturated internet connection, however, it cannot recover the bandwidth already consumed before traffic reaches the gateway.
WAF+ adds application-aware protection for websites, web applications, and APIs. Its official specifications document integrated DDoS protection across Layers 3–7 and granular restrictions by user, URL path, and specific URL. These controls are particularly relevant to HTTP/HTTPS-based DDoS attacks: appropriately configured rules can block identified attacking requests before they reach the protected application.
Why managed WAF rules matter during an attack
Application-layer DDoS protection requires attention to requests that can look superficially legitimate. With an unmanaged WAF, customers must configure and maintain their own policies. Network Box USA's WAF+ is fully managed by its 24/7 Security Operations Center (SOC), which handles rule configuration, monitoring, and ongoing tuning on the customer's behalf. When attacking traffic is identified, the security team can configure targeted rules and review their effect on legitimate application use.
The WAF+ overview also includes cloud-based DDoS support with real-time human SOC assistance during attacks. This managed DDoS protection combines filtering with people responsible for operating it; it does not mean every attack is automatically identified or can be eliminated by adding a rule.
Deployment still determines where filtering takes effect. Network Box USA's WAF architecture diagram shows HTTPS requests passing through WAF+ to protected origin servers, with direct origin access restricted. A cloud-hosted WAF positioned upstream of the customer's connection can filter requests before they consume that link's capacity, provided the relevant application traffic is routed through it. A WAF behind the constrained connection faces the same bandwidth limit as a local gateway. Confirm the actual routing, filtering location, and capacity in the proposed deployment.
Check separately whether a proposal covers a public website, remote-access services, or an entire network connection. Application protection does not establish coverage for every other service sharing the link, or for floods sent directly to the customer's public addresses. Keep upstream or cloud-based mitigation before the constrained connection part of the service design.
Is URL filtering part of DDoS protection?
Yes, URL-based request filtering can contribute to application-layer DDoS protection. Traditional Secure Web Gateway URL filtering controls which websites users can access. WAF URL filtering instead inspects incoming HTTP/HTTPS requests and applies security policies to specific URLs, paths, and application endpoints.
Network Box USA's WAF+ supports these granular restrictions, allowing malicious or abusive requests to be blocked according to configured policies. Its 24/7 SOC manages rule configuration, monitoring, and tuning. URL filtering and DDoS protection therefore overlap at the application layer, but URL-based filtering alone cannot prevent a volumetric attack from saturating an internet connection.
An ISP escalation worksheet
Prepare this record before an incident so the team can identify the congested path and reach the party able to act upstream.
| Field | What to record |
|---|---|
| Circuit and contacts | Provider, circuit identifier, support number, escalation route, and authorized requester. |
| Observed impact | Start time and time zone, affected services, baseline versus current utilization, and loss observations. |
| Upstream options | Contracted mitigation service, activation conditions, routing dependencies, and expected communications. |
| Acceptance | Application recovery, residual loss, mitigation status, and the owner of the post-incident review. |
Bring the network boundary into the review
Plan the layers together: UTM+ for local network-layer protection, SOC-managed WAF+ for application-aware DDoS defenses, and upstream mitigation before a constrained internet connection. Review the actual traffic paths, capacity, and provider responsibilities so each protection has a defined role.
For a discussion of your gateway, internet connections, and the handoff between providers, contact our team.