
Branches, Cloud, Remote users, VPN, Failover, Reporting.
Services · Prevent
Managed Secure SD-WAN Services
Connect distributed work without fragmenting security.
Secure SD-WAN helps headquarters, branches, cloud services, and remote teams stay connected under centralized security policy.
What changes
The control matters. The ownership around it matters more.
Path selection, Failover, Encrypted tunnels, Branch visibility, Policy support.
Improve branch uptime, Control cloud traffic, Centralize policy, Support remote work.
Service definition
What Secure SD-WAN does.
Managed Secure SD-WAN combines resilient, policy-based connectivity with firewall, intrusion prevention, encrypted tunnels, traffic visibility, and continuous operational support for distributed locations.
- Organizations connecting branches, cloud services, headquarters, and remote environments
- Teams that need link failover and traffic optimization without a separate security stack
- MSPs standardizing secure connectivity across multiple customer locations
- Unreliable links that interrupt access to cloud and business applications
- Separate networking and security policies that drift over time
- Limited visibility across distributed sites and circuits
- Manual failover, routing, VPN, and appliance-management overhead
Architecture diagram
See how branches connect.
Explore encrypted branch-to-hub connections, internet routing, and the optional disaster recovery hub behind a resilient SD-WAN deployment.
Explore the full diagram, or download its single-page PDF for review and printing.
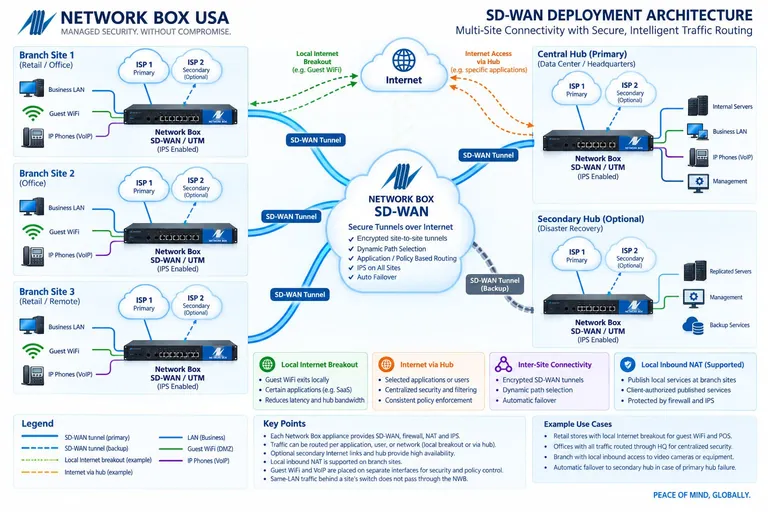
SD-WAN
Branch connectivity, central hubs, traffic routing, and failover.
Product details
Evaluate the capabilities that matter in your environment.
More than traffic routing, the service combines SD-WAN capabilities with a managed security device.
Dynamic routing and automatic link monitoring help optimize connectivity across distributed sites.
Central policy, logs, firewall, IPS, VPN, and 24/7 monitoring remain coordinated in one service.
Managed from day one
One continuous operating motion.
Deployment is the beginning of the service, not the end of the project.
- 01Assess the environment
Review the sites, users, systems, traffic flows, obligations, current controls, and operating constraints that shape the service.
- 02Design the coverage
Define in-scope assets, policies, integrations, retention, escalation paths, responsibilities, and success measures before deployment.
- 03Deploy and tune
Connect or install the service, validate traffic and telemetry, test policy behavior, resolve exceptions, and document the operational handoff.
- 04Monitor and respond
Operate, update, tune, review, and escalate the subscribed controls according to the agreed monitoring and support scope.
- 05Report and improve
Review activity, evidence, exceptions, service trends, and recommended next priorities with ownership made clear.
Choose the right layer
How this service differs from adjacent coverage.
These services work together, but they solve different operational problems.
Compared with Unified Threat Management
UTM+ centers on consolidated gateway security. Secure SD-WAN adds path selection, link health, failover, and multi-site connectivity to the managed edge controls.
Compared with Secure Web Gateway
A Secure Web Gateway governs user web access and content. Secure SD-WAN governs how sites and applications connect across available network paths.
Related coverage
Security works better when the layers work together.
Included with Secure SD-WAN
The service, clearly accounted for.
Review the protection, operating support, and service capabilities included in the offering.
20included
capabilities
capabilities
01
Connectivity and edge security
- Dynamic routing and automatic link monitoring
- Next-generation firewall with stateful inspection, packet filtering, NAT, and advanced routing
- Frontline, inline, and infected-LAN intrusion prevention
- Layer 3 DDoS protection
- IPsec, PPTP, SSL, and WireGuard VPN
- DHCP and optional DNS services
- Application identification
- Bidirectional IPv4 and IPv6 translation across Layers 3–7
02
Traffic control and visibility
- Web-traffic proxy
- Anti-malware protection for HTTP, HTTPS, and FTP
- URL antivirus scanning
- Layer 3 and Layer 7 quality of service
- Customizable log portal and reporting
03
Managed-service layer
- 24×7×365 monitoring and PUSH security updates
- Standard service-level agreement
- 24×7 Security Operations Center
- SIEM with 90 days of rolling logs and one year of cold storage
- Security Response Center threat research
- Four ISO certifications and PCI DSS attestation
- Intelligence from more than 70 threat partners
Put the guidance to work
Start with a practical security review.
Before adding connected devices to your network, use our secure IoT procurement checklist to review their security requirements.
Buyer’s guide
Commercial scope and compliance context.
Evaluate the complete operating commitment, not only a license or feature list.
A defined managed scope
Pricing depends on the number of sites, circuits, bandwidth and throughput needs, redundancy design, VPN requirements, managed security controls, and support scope. The proposal should make implementation, monitoring, updates, reporting, and any optional connectivity work explicit.
Compare the full operating cost →Technical support, not a compliance guarantee
No single product establishes compliance. These guides show where the service can support controls, operations, and evidence.
Service FAQ
Questions buyers ask about Secure SD-WAN.
What is Secure SD-WAN?
Managed Secure SD-WAN combines resilient, policy-based connectivity with firewall, intrusion prevention, encrypted tunnels, traffic visibility, and continuous operational support for distributed locations.
Who is Secure SD-WAN designed for?
Common fits include organizations connecting branches, cloud services, headquarters, and remote environments, teams that need link failover and traffic optimization without a separate security stack, and mSPs standardizing secure connectivity across multiple customer locations.
What does Network Box USA manage?
The managed scope includes path selection, failover, encrypted tunnels, branch visibility, and policy support. Exact responsibilities, coverage, escalation, and exclusions are confirmed during solution design.
How does Secure SD-WAN differ from Unified Threat Management?
UTM+ centers on consolidated gateway security. Secure SD-WAN adds path selection, link health, failover, and multi-site connectivity to the managed edge controls.
How is Secure SD-WAN priced?
Pricing depends on the number of sites, circuits, bandwidth and throughput needs, redundancy design, VPN requirements, managed security controls, and support scope. The proposal should make implementation, monitoring, updates, reporting, and any optional connectivity work explicit.
Does Secure SD-WAN make an organization compliant?
No single security service establishes compliance. Secure SD-WAN can support technical controls and evidence associated with NIST CSF, CIS Controls v8.1, CMMC, PCI DSS, HIPAA, and SOC 2, but applicability, governance, policies, complete scope, remediation, and any assessment or certification remain the organization’s responsibility.
Security stack review
See where Secure SD-WAN belongs in your environment.
Start with your current controls, operating constraints, and the risks you most need to reduce.
Request a Security Stack Review