
Firewall, IPS, VPN, Malware, Policy, Support.
Services · Prevent
Managed Unified Threat Management (UTM+)
The essential edge controls, unified and managed.
UTM+ brings firewall, intrusion prevention, VPN, malware filtering, and policy controls into one managed edge security service.
Based in Houston. Serving organizations and MSPs across North America.
What changes
The control matters. The ownership around it matters more.
Firewall, IPS, VPN, Gateway controls, Threat updates.
Consolidate controls, Block known threats, Simplify operations, Strengthen policy.
Service definition
What Unified Threat Management does.
Managed Unified Threat Management combines firewall, intrusion prevention, VPN, malware inspection, traffic policy, logging, updates, and operational support in one coordinated security gateway.
- Organizations consolidating several perimeter-security appliances and consoles
- Small and midsize teams that need enterprise gateway controls without additional specialists
- MSPs seeking a repeatable managed edge platform for customer environments
- Gaps between separately configured firewall, IPS, VPN, and malware controls
- Appliances that fall behind on signatures, policy, tuning, or review
- Limited inbound and outbound traffic visibility
- Operational overhead from multiple vendors, renewals, and escalation paths
Architecture diagram
See the gateway in your network.
Follow the perimeter connections between internet providers, the managed firewall, internal networks, and an optional DMZ.
Explore the full diagram, or download its single-page PDF for review and printing.
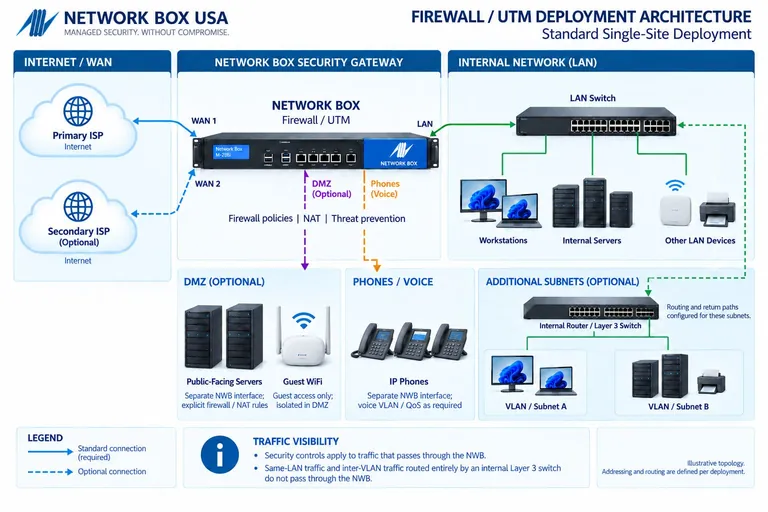
Firewall / UTM
Single-site perimeter, internal networks, and optional DMZ connections.
Product details
Evaluate the capabilities that matter in your environment.
Firewall, intrusion prevention, VPN, malware filtering, and application policy operate in one managed gateway.
Single-pass architecture is designed to reduce latency and duplicated inspection overhead.
Pricing is presented as predictable, with no additional full-time security staff required.
Managed from day one
One continuous operating motion.
Deployment is the beginning of the service, not the end of the project.
- 01Assess the environment
Review the sites, users, systems, traffic flows, obligations, current controls, and operating constraints that shape the service.
- 02Design the coverage
Define in-scope assets, policies, integrations, retention, escalation paths, responsibilities, and success measures before deployment.
- 03Deploy and tune
Connect or install the service, validate traffic and telemetry, test policy behavior, resolve exceptions, and document the operational handoff.
- 04Monitor and respond
Operate, update, tune, review, and escalate the subscribed controls according to the agreed monitoring and support scope.
- 05Report and improve
Review activity, evidence, exceptions, service trends, and recommended next priorities with ownership made clear.
Choose the right layer
How this service differs from adjacent coverage.
These services work together, but they solve different operational problems.
Compared with Edge Defense
UTM+ is the managed gateway at the center of perimeter enforcement. Edge Defense is the wider architecture that can combine UTM+ with web, branch, and application-specific controls.
Compared with Secure SD-WAN
UTM+ prioritizes consolidated security inspection. Secure SD-WAN adds dynamic path selection, link monitoring, and failover for distributed connectivity.
Related coverage
Security works better when the layers work together.
Included with Unified Threat Management
The service, clearly accounted for.
Review the protection, operating support, and service capabilities included in the offering.
23included
capabilities
capabilities
01
Gateway protection
- Next-generation firewall with stateful inspection, packet filtering, NAT, and advanced routing
- Frontline, inline, and infected-LAN intrusion prevention
- Layer 3 DDoS protection
- IPsec, PPTP, and SSL VPN
- Optional DNS server
- Application identification
- Bidirectional IPv4 and IPv6 translation across Layers 3–7
- Web-traffic proxy
02
Inspection and policy
- Anti-malware protection for HTTP, HTTPS, and FTP
- URL antivirus scanning
- Layer 3 and Layer 7 quality of service
- Network Box Antivirus with Z-Scan
- Kaspersky or Bitdefender antivirus protection
- S-Scan content filtering
- IP-, entity-, and LDAP-based policy enforcement
- Customizable log portal and reporting
03
Managed-service layer
- 24×7×365 monitoring and PUSH security updates
- Standard service-level agreement
- 24×7 Security Operations Center
- SIEM with 90 days of rolling logs and one year of cold storage
- Security Response Center threat research
- Four ISO certifications and PCI DSS attestation
- Intelligence from more than 70 threat partners
Illustrative planning example
Accept a gateway policy change
A branch needs a new application connection while guest devices must remain separated.
- Define the path
- Record source, destination, protocol, address family, application owner, and permitted purpose.
- Test both outcomes
- Verify the required transaction succeeds and the prohibited guest-to-business path remains blocked.
- Record acceptance
- Capture the enforcing rule, log evidence, change approval, rollback conditions, and business acceptance.
This is a planning example, not a customer incident or a promise that a particular product integration is supported. Confirm the actual scope during service design.
Use the dual-stack acceptance matrix →Explore the decisions behind the service
Practical Unified Threat Management guidance.
Network Box firewall and IPS
Understand the controls behind the managed gateway.
Can you remove a firewall rule with zero hits?
Review rule dependencies before changing production policy.
Check both IPv4 and IPv6 policy
Validate the same permitted and denied paths in both address families.
Test existing connections during failover
Identify state, routing, and shared infrastructure dependencies.
See the operating evidence
Read an actual redacted KPI report.
The published sample includes period comparisons for device utilization, network activity, and security metrics. Its April 2025 reporting period makes it an example of the reporting format, not a current measurement of your environment.
- Capacity and workload
- CPU, memory, disk, and workload measurements help frame a capacity discussion.
- Traffic and connections
- Internet, LAN, DMZ, VPN, and connection views help identify the paths covered by the report.
- Period and context
- Compare the same metric and reporting period, then connect changes to configuration, incidents, and business activity.
Agree which sources and reports belong in your service scope. A KPI summary, an incident investigation, and an onboarding acceptance record answer different questions.
Open the redacted KPI report (PDF)Buyer’s guide
Commercial scope and compliance context.
Evaluate the complete operating commitment, not only a license or feature list.
A defined managed scope
Scope depends on locations, traffic capacity, deployment model, VPN and policy requirements, logging, reporting, and support. The managed proposal should make gateway technology, deployment, security updates, monitoring, reporting, and support visible as one operating cost.
Compare the full operating cost →Technical support, not a compliance guarantee
No single product establishes compliance. These guides show where the service can support controls, operations, and evidence.
UTM readiness assessment
Unified Threat Management scorecard
How well is your network perimeter and core traffic protected?
Self-guided review7 questions
Answer seven questions about the controls, consistency, and monitoring surrounding your network edge.
0/100
Your point-in-time result
Review in progress
Service FAQ
Questions buyers ask about Unified Threat Management.
What is Unified Threat Management?
Managed Unified Threat Management combines firewall, intrusion prevention, VPN, malware inspection, traffic policy, logging, updates, and operational support in one coordinated security gateway.
Who is Unified Threat Management designed for?
Common fits include organizations consolidating several perimeter-security appliances and consoles, small and midsize teams that need enterprise gateway controls without additional specialists, and mSPs seeking a repeatable managed edge platform for customer environments.
What does Network Box USA manage?
The managed scope includes firewall, ips, vpn, gateway controls, and threat updates. Exact responsibilities, coverage, escalation, and exclusions are confirmed during solution design.
How does Unified Threat Management differ from Edge Defense?
UTM+ is the managed gateway at the center of perimeter enforcement. Edge Defense is the wider architecture that can combine UTM+ with web, branch, and application-specific controls.
How is Unified Threat Management priced?
Scope depends on locations, traffic capacity, deployment model, VPN and policy requirements, logging, reporting, and support. The managed proposal should make gateway technology, deployment, security updates, monitoring, reporting, and support visible as one operating cost.
Does Unified Threat Management make an organization compliant?
No single security service establishes compliance. Unified Threat Management can support technical controls and evidence associated with NIST CSF, CIS Controls v8.1, CMMC, PCI DSS, HIPAA, and SOC 2, but applicability, governance, policies, complete scope, remediation, and any assessment or certification remain the organization’s responsibility.
What is the difference between a firewall and unified threat management?
A firewall controls permitted network connections. Unified threat management combines that function with controls such as intrusion prevention, VPN, malware inspection, and web or application policy. Product labels overlap, so compare the enabled controls, inspected throughput, updates, monitoring, and who manages changes. Network Box USA UTM+ includes the managed operating work around the gateway.
How should we size a managed UTM gateway?
Start with internet bandwidth, concurrent users and connections, VPN traffic, and the inspection features you need. Evaluate capacity with those controls enabled, including any HTTPS inspection, rather than using basic firewall throughput alone. Document growth, high availability, maintenance windows, and the traffic paths that could bypass inspection during service design.
Security stack review
See where Unified Threat Management belongs in your environment.
Start with your current controls, operating constraints, and the risks you most need to reduce.
Request a Security Stack Review